Disgruntled Researcher Releases New Windows Zero-Day Flaw
An independent researcher has publicly disclosed a Windows zero-day vulnerability dubbed SignDrop, which can elevate local user privileges to System rights.
 ⚖️Regulation & Policy
Photo: Ars Technica Tech
Key points
- Researcher Nightmare Eclipse disclosed the SignDrop Windows zero-day vulnerability.
- The flaw permits local users to achieve full System rights by abusing Windows Defender and logging functions.
- Independent verification by Will Dormann confirmed the exploit works under specific version and age requirements.
A security researcher operating under the pseudonym Nightmare Eclipse has disclosed a fresh Windows zero-day vulnerability named SignDrop. The flaw affects the Common Log File System in certain versions of Windows, allowing attackers with standard user rights to escalate their privileges to full System access by manipulating system components and leveraging Windows Defender.
How the SignDrop Exploit Operates
The attack mechanism abuses a legitimate Windows Defender function meant for processing antivirus signature updates. By manipulating Windows Object Manager symbolic links, an attacker forces Defender to open a crafted log file container under the security context of the antimalware engine. Because of how file permissions and the logging service interact, the operation creates a file with elevated privileges that can be abused for privilege escalation.
Ironically, the flaw stems from a security mitigation that Microsoft implemented in October 2025 to block earlier exploits targeting the logging system. The researcher noted that the logic behind the mitigation can be turned against itself, potentially bypassing antivirus and Endpoint Detection and Response tamper protection mechanisms.
Verification and Affected Systems
Independent researcher Will Dormann confirmed that he successfully reproduced the exploit, noting that it functions on specific configurations of Windows 11 version 26H2 and Windows Server 2025 Experimental. However, Dormann pointed out that exploitation requires specific conditions, including a system installation older than 90 days and a particular registry authentication mode configuration. Microsoft representatives did not respond to requests for comment regarding the disclosure.
Source Ars Technica Tech — arstechnica.com/security/2026/11/windows-0-day-dropped-by-disgruntled-r… ↗
Read next
 🧠AI Analysis
Pedestal AI Secures Seed Funding to Automate Logistics With Intelligent Agents
Pedestal AI has launched publicly with $4.7 million in seed backing to deploy agentic artificial intelligence aimed at streamlining logistics and supply chain operations.
 🏢Big Tech
United Launch Alliance Investigates Vulcan Rocket Failure
United Launch Alliance is investigating a mission failure of its Vulcan rocket, which suffered from low booster performance shortly after liftoff. The incident raises que…
 🌐Work & Society
US Southwest Hydropower Output Hits Record Lows Amid Persistent Drought
Hydropower generation in the US Southwest dropped 28% below the 10-year average this summer as record-low water levels in the Colorado River Basin threaten regional energ…
 🏢Big Tech
YouTube Updates View Metrics to Include TV Co-Viewing Estimates
YouTube is incorporating estimated co-viewing data into its public view counts to better reflect group consumption on television sets.
 🏢Big Tech
Apple Services Experience Widespread Outage
Apple users are reporting significant disruptions across iCloud, the App Store, and other core services, despite initial discrepancies in the company's status reporting.
 🌐Work & Society
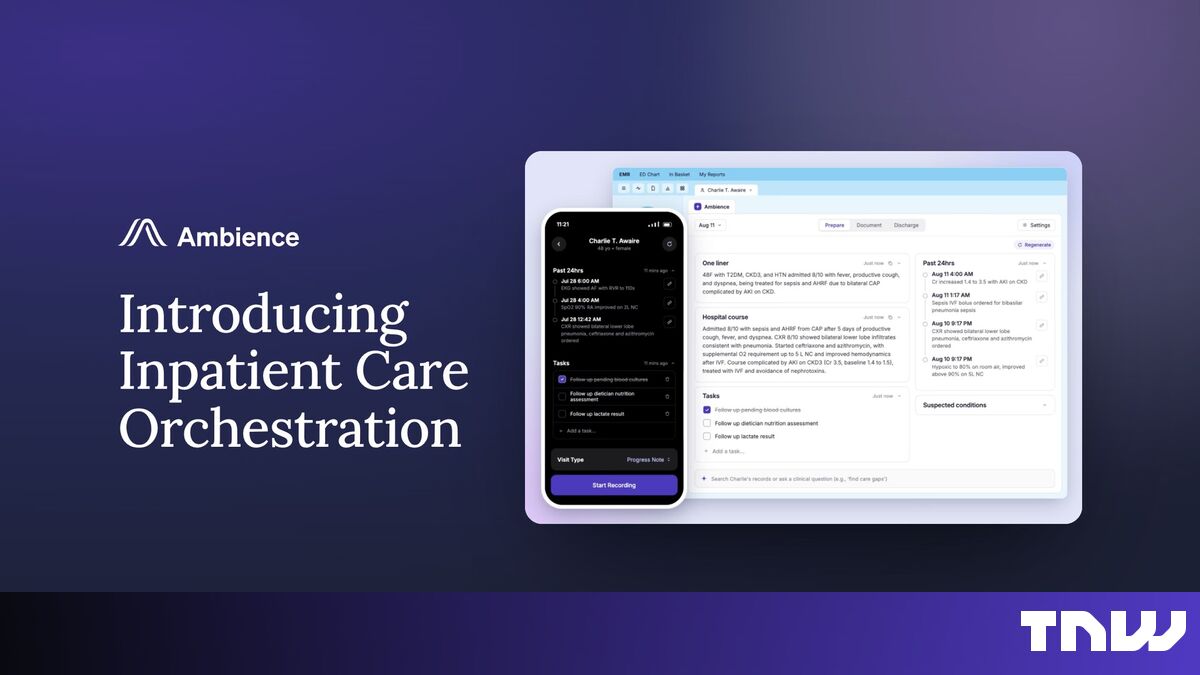
Ambience Healthcare Expands Clinical AI Suite for Hospital Operations
Ambience Healthcare has launched new AI tools designed to assist hospital staff with patient rounding and discharge planning, aiming to improve both clinical efficiency a…