Optimizely Tag Layer Compromise Exposes Millions of Visitors to Crypto Clippers and Card Skimmers
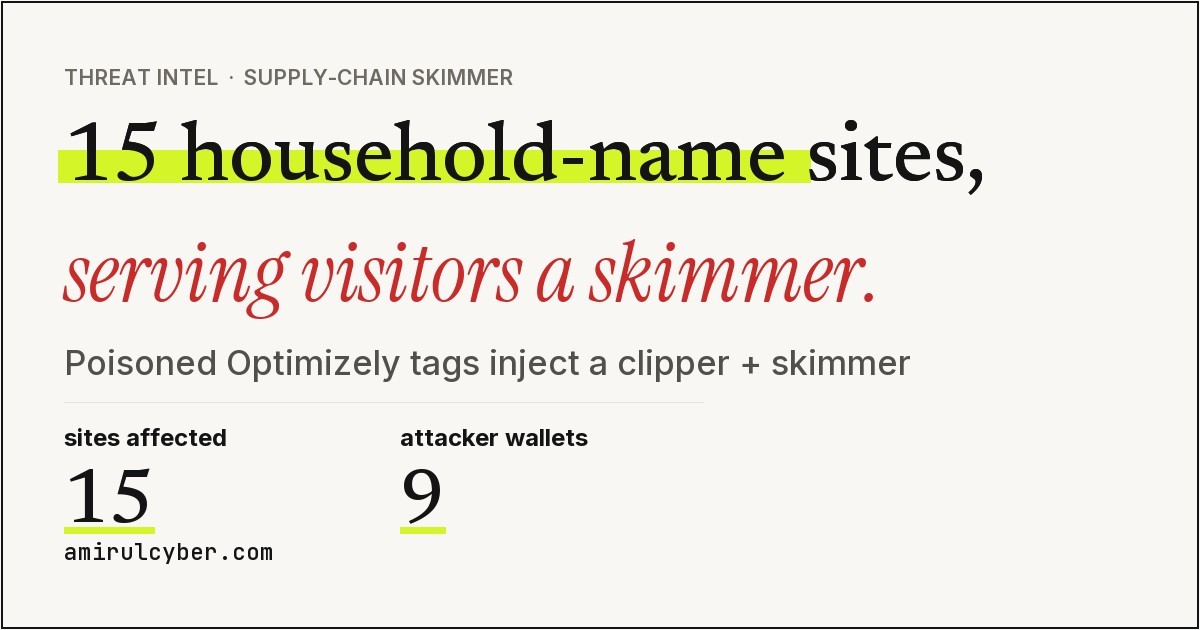
A sophisticated supply-chain attack compromised Optimizely tag layers, injecting malicious scripts that target visitors of major global websites including CNN, BBC, and Zoom.
 🧠AI Analysis
Photo: Hacker News Front Page
Key points
- Fifteen major websites impacted via compromised Optimizely tag layers
- Payload includes crypto-clippers, card skimmers, and data exfiltration tools
- Attacks target browser-level interactions without requiring server-side breaches
A major supply-chain security incident has impacted at least 15 high-profile websites, exposing millions of visitors to malicious JavaScript injected directly into Optimizely tag bundles. Affected platforms include household names such as CNN, Zoom, Fox News, BBC, Salesforce, GitLab, American Eagle, and Hootsuite. Security analysts report that the attack operates at the tag layer, meaning that a website's origin servers can remain entirely clean while visitors are actively targeted by malicious code.
The injected payload packs multiple aggressive capabilities, including a multi-currency crypto-clipper, a credit card skimmer, a data exfiltration tool capturing cookies and screenshots, and a specific iOS second-stage vector. The crypto-clipper uses advanced regex and checksum validation to swap cryptocurrency wallet addresses across numerous blockchains right in the user's browser, while the card skimmer intercepts payment forms and validates entries using Luhn and brand checks. Additional vectors target iOS devices up to iOS 18.6 with hidden iframes and obfuscated scripts.
Organizations utilizing Optimizely have been urged to immediately inspect their served bundles for unauthorized project IDs, monitor Content-Security-Policy script-src violations for unknown hosts, and run staging tests to verify payment inputs. While a few sites successfully blocked the script using CSP rules, millions of users across the affected platforms remain in the immediate blast radius.
What to watch next: Further disclosures from affected enterprises regarding patch timelines and the full scope of the exploited tag infrastructure.
Source Hacker News Front Page — amirulcyber.com/2026/11/16/optimjack-optimizely-skimmer/ ↗
Read next
 🏢Big Tech
United Launch Alliance Investigates Vulcan Rocket Failure
United Launch Alliance is investigating a mission failure of its Vulcan rocket, which suffered from low booster performance shortly after liftoff. The incident raises que…
 🌐Work & Society
US Southwest Hydropower Output Hits Record Lows Amid Persistent Drought
Hydropower generation in the US Southwest dropped 28% below the 10-year average this summer as record-low water levels in the Colorado River Basin threaten regional energ…
 🏢Big Tech
YouTube Updates View Metrics to Include TV Co-Viewing Estimates
YouTube is incorporating estimated co-viewing data into its public view counts to better reflect group consumption on television sets.
 ⚖️Regulation & Policy
OpenAI Partners with Chilean Ministry to Advance Public Sector AI
OpenAI has signed a non-binding agreement with Chile's science ministry to integrate artificial intelligence into public administration and support local startups.
 🌐Work & Society
Ambience Healthcare Expands Clinical AI Suite for Hospital Operations
Ambience Healthcare has launched new AI tools designed to assist hospital staff with patient rounding and discharge planning, aiming to improve both clinical efficiency a…
 ⚖️Regulation & Policy
AWS Highlights Enterprise Governance and AI Workspace Quick Ahead of re:Invent 2026
Amazon Web Services is spotlighting its workplace AI platform, AWS Quick, ahead of its upcoming re:Invent 2026 conference, emphasizing secure deployment across major ente…