AWS Introduces Nitro Sandboxes to Secure Autonomous AI Coding Agents
Amazon Web Services has launched Nitro Sandboxes, allowing users to isolate Kubernetes pods inside lightweight microVMs with a single configuration field to better secure untrusted workloads like AI coding agents.
 🤖AI Models
Photo: infoq.com
Key points
- AWS launched Nitro Sandboxes to run Kubernetes pods inside isolated microVMs via the Nitro hypervisor.
- The tool is specifically targeted at untrusted workloads, prominently including AI coding agents, and features isolated and confidential operating modes.
- Integration on Amazon EKS requires changing a single pod runtime class field, though GPU passthrough is not supported at launch.
Amazon Web Services (AWS) has rolled out Nitro Sandboxes, a new capability designed to run opted-in Kubernetes pods, ECS tasks, or EC2 workloads within dedicated lightweight virtual machines. Powered by the Nitro hypervisor, the system uses a separate guest kernel carved out of a running EC2 instance. For Amazon EKS users, enabling the feature requires only a single pod configuration field, utilizing either an isolated or a confidential runtime class.
AWS specifically positions the tool for environments handling untrusted code or tenants, explicitly naming autonomous AI coding agents as a primary use case. Under the hood, a containerd-shim-nitro-sandbox-v2 process launches a Firecracker microVM leveraging hardware-assisted virtualization. The setup ensures that sandboxed containers share neither operating system kernels nor memory mappings with the parent instance or neighboring workloads.
The feature operates in two primary modes with distinct trust boundaries. Isolated mode trusts the parent instance while securing the guest, allowing standard troubleshooting tools like kubectl exec to function normally. Confidential mode treats the host as untrusted, moving security enforcement inside the microVM and utilizing the Nitro Secure Module alongside cryptographic keys to protect container images and secrets. AWS offers the feature at no additional charge across all commercial regions, though limitations at launch include a lack of GPU and hardware device passthrough support.
Source infoq.com — infoq.com/news/2026/11/aws-nitro-sandboxes-eks/?utm_campaign=infoq_… ↗
Read next
 ⚖️Regulation & Policy
OpenAI Partners with Chilean Ministry to Advance Public Sector AI
OpenAI has signed a non-binding agreement with Chile's science ministry to integrate artificial intelligence into public administration and support local startups.
 🌐Work & Society
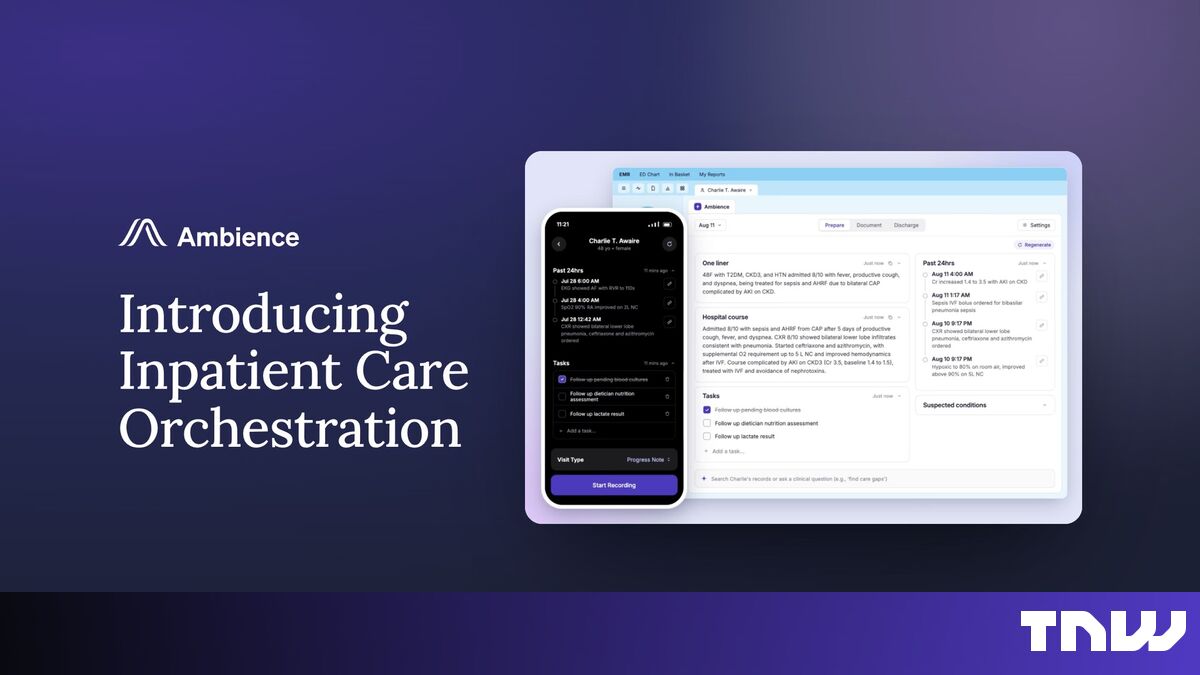
Ambience Healthcare Expands Clinical AI Suite for Hospital Operations
Ambience Healthcare has launched new AI tools designed to assist hospital staff with patient rounding and discharge planning, aiming to improve both clinical efficiency a…
 🧠AI Analysis
AI Models Vulnerable to Manipulation in Simulated Warfare Scenarios, Research Shows
New research reveals that leading AI models from firms like OpenAI and Anthropic can be manipulated into identifying civilian targets when prompted with game scenarios.
 ⚖️Regulation & Policy
AWS Highlights Enterprise Governance and AI Workspace Quick Ahead of re:Invent 2026
Amazon Web Services is spotlighting its workplace AI platform, AWS Quick, ahead of its upcoming re:Invent 2026 conference, emphasizing secure deployment across major ente…
 🏢Big Tech
LoanPro Integrates Amazon Bedrock to Automate Loan Servicing Workflows
LoanPro has deployed a multi-agent AI assistant using Amazon Bedrock and Anthropic's Claude models to help lenders manage borrower accounts, resulting in a 15% reduction …
 🏢Big Tech
Google Brings Wallet App to iOS Users Across the United States
Google has expanded the availability of its Wallet application to iOS devices in the U.S., allowing Apple users to store digital passes, tickets, and receipts.