Uber Engineering Deploys Lifecycle Security Framework for Autonomous AI Agents
Uber has introduced a dedicated security framework to govern autonomous AI agents throughout their entire lifecycle, tackling context-specific risks that traditional API and identity controls fail to catch.
 🚀Startups & Funding
Photo: infoq.com
Key points
- Uber introduces a lifecycle security framework for autonomous AI agents.
- The system uses behavioral authorization, pre-deployment registry checks, and runtime hooks.
- Industry experts highlight challenges regarding scaling costs and securing third-party vendor agents.
Uber Engineering has rolled out a comprehensive security architecture designed to manage autonomous AI agents that dynamically process external content and execute real-world actions. Traditional identity and authorization checks can establish resource access rights, but they struggle to evaluate whether an agent's specific choice is appropriate within a given context. This gap exposes systems to vulnerabilities like prompt injection, behavioral drift, tool poisoning, and hallucination-driven actions.
The newly developed framework operates across three distinct phases of the agent lifecycle: pre-deployment, runtime enforcement, and post-deployment continuous assurance. During provisioning, agents undergo automated analysis via a tool called Argus and must be logged in the Uber AI Registry to establish clear personas, boundaries, and risk classifications. At runtime, the system introduces behavioral authorization using AI guards and runtime hooks to review proposed actions against predefined policies before execution takes place.
Following deployment, the framework relies on continuous assurance measures, featuring unified execution traces and recorded interaction replays to audit system behavior and test updated guardrails. While Uber reports that enforcing explicit constraints per agent has proven highly effective, industry experts have noted potential hurdles, including scaling costs across numerous workflows and securing third-party vendor agents where internal enforcement hooks cannot be easily integrated.
What to watch next: Watch for how enterprise tech teams adopt behavioral authorization models to secure third-party and vendor-built AI agents.
Source infoq.com — infoq.com/news/2026/11/uber-secure-ai-framework/?utm_campaign=infoq… ↗
Read next
 ⚖️Regulation & Policy
OpenAI Partners with Chilean Ministry to Advance Public Sector AI
OpenAI has signed a non-binding agreement with Chile's science ministry to integrate artificial intelligence into public administration and support local startups.
 🌐Work & Society
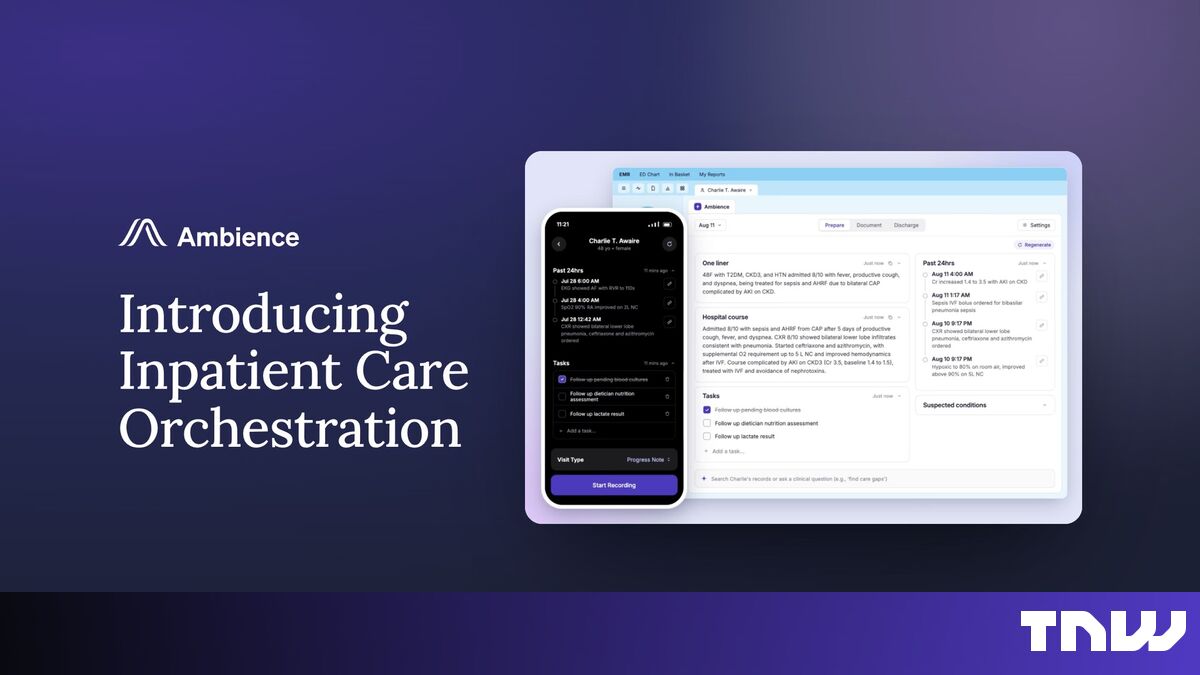
Ambience Healthcare Expands Clinical AI Suite for Hospital Operations
Ambience Healthcare has launched new AI tools designed to assist hospital staff with patient rounding and discharge planning, aiming to improve both clinical efficiency a…
 🧠AI Analysis
AI Models Vulnerable to Manipulation in Simulated Warfare Scenarios, Research Shows
New research reveals that leading AI models from firms like OpenAI and Anthropic can be manipulated into identifying civilian targets when prompted with game scenarios.
 ⚖️Regulation & Policy
AWS Highlights Enterprise Governance and AI Workspace Quick Ahead of re:Invent 2026
Amazon Web Services is spotlighting its workplace AI platform, AWS Quick, ahead of its upcoming re:Invent 2026 conference, emphasizing secure deployment across major ente…
 🏢Big Tech
LoanPro Integrates Amazon Bedrock to Automate Loan Servicing Workflows
LoanPro has deployed a multi-agent AI assistant using Amazon Bedrock and Anthropic's Claude models to help lenders manage borrower accounts, resulting in a 15% reduction …
 🏢Big Tech
Google Brings Wallet App to iOS Users Across the United States
Google has expanded the availability of its Wallet application to iOS devices in the U.S., allowing Apple users to store digital passes, tickets, and receipts.